CaseStudy
- title
- summary
- role
- status
- stack
- sections
- may
- quote verbatim · summarize · link to sections
- may not
- invent metrics · speak for past employers · expose gated content
One Portal Sign-In
Five separate sign-in experiences replaced by one role-adaptive authentication system for B2B and B2C users of an enterprise insurance platform.
Summary
- problem
- approach
- impact
- may
- quote verbatim
- may not
- round or extrapolate results
At a glance
- Problem
- With five disconnected sign-in experiences, many users couldn't tell which portal was theirs. Clients logged in to the wrong one often enough to take up a meaningful share of support time, and new users abandoned registration entirely.
- Approach
- One sign-in with 2FA, a dashboard that adapts to the user's role after sign-in, and contextual support built into the portal.
- Impact
- Authentication success rose substantially. Session duration grew and support volume dropped. Legacy policy access remained simple for existing users.
Problem
Five separate sign-in experiences.
Cognitive overload
Multiple credentials per role, inconsistent interfaces, no single mental model.
Wrong-portal logins
A meaningful share of clients logged into the wrong portal every month, taking up a substantial share of support capacity.
Abandonment
New users abandoned registration entirely on the portal-selection step.
The organization operated five disconnected sign-in experiences across B2B and B2C touchpoints. Each user role had its own portal, credentials, and layout, so users struggled before they ever reached the product.
Users
Five user types on one sign-in.
Five user types
- Individual policy holders
- Business/B2B clients
- Customer service representatives
- Agents
- Back-office administrators
Share
One sign-in
Each user type had its own permission set and needed something different as soon as the session started.
Process
22 weeks and 47 user interviews.
22 weeks
Research included 47 user interviews across all five roles.
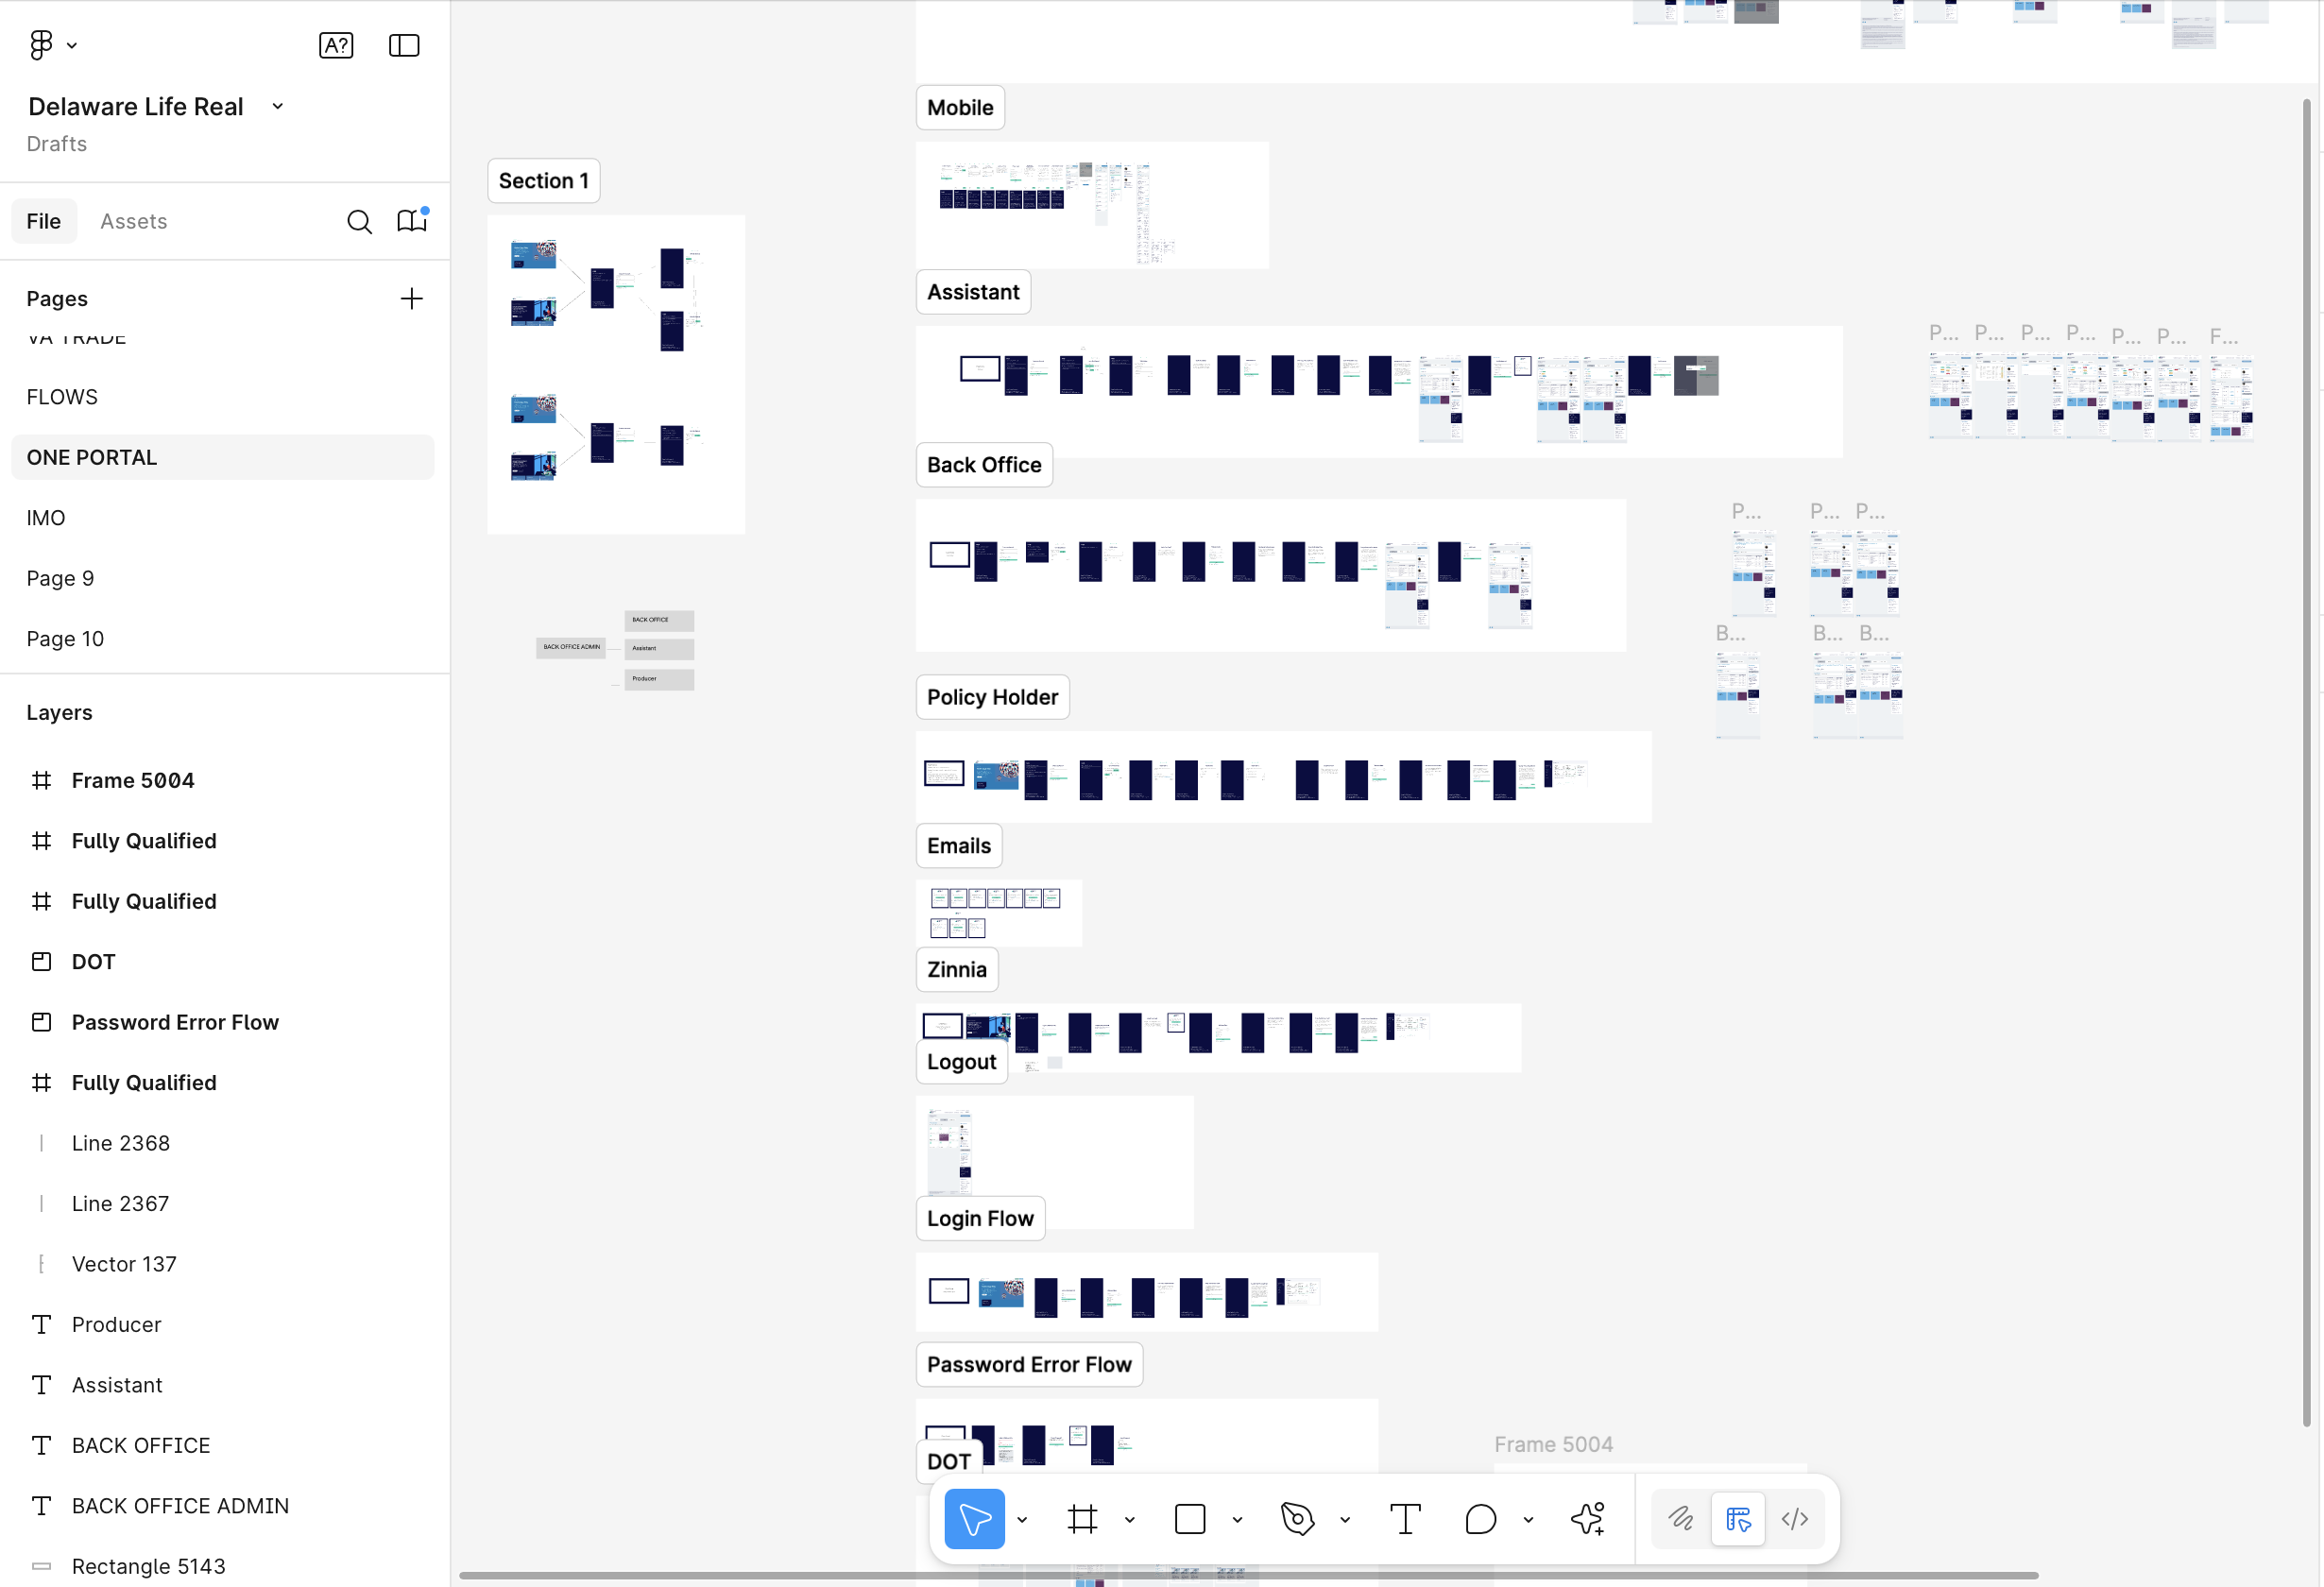
I led the design from start to finish: research, information architecture, visual design system, user testing, and engineering handoff.
- research ecosystem mapping; 2FA integration specs.
- information architecture journey mapping and flow work to find clear entry and exit points.
- visual design a design system and high-fidelity prototypes for each role.
- user testing moderated Fullstory sessions across all five roles with iterative refinement.
- implementation spec docs, design reviews, and QA testing while engineering built it.
Solution
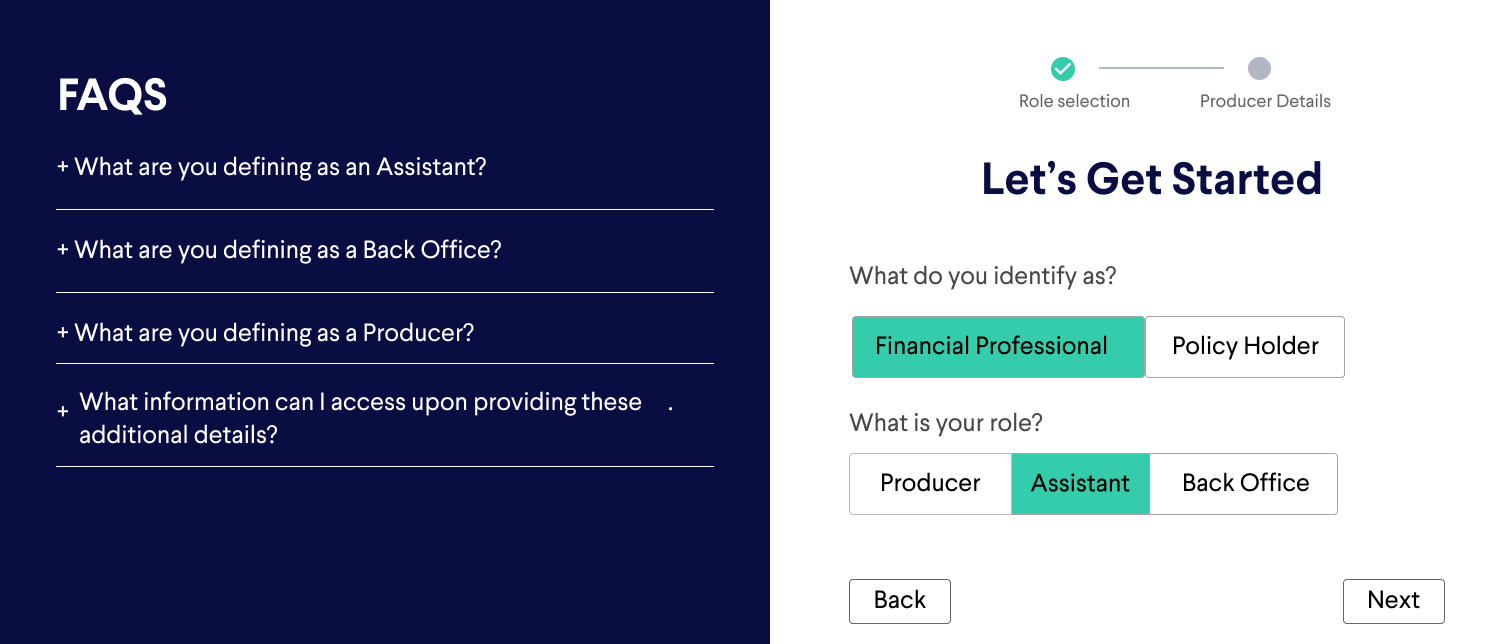
One sign-in, then a dashboard that adapts to each role.
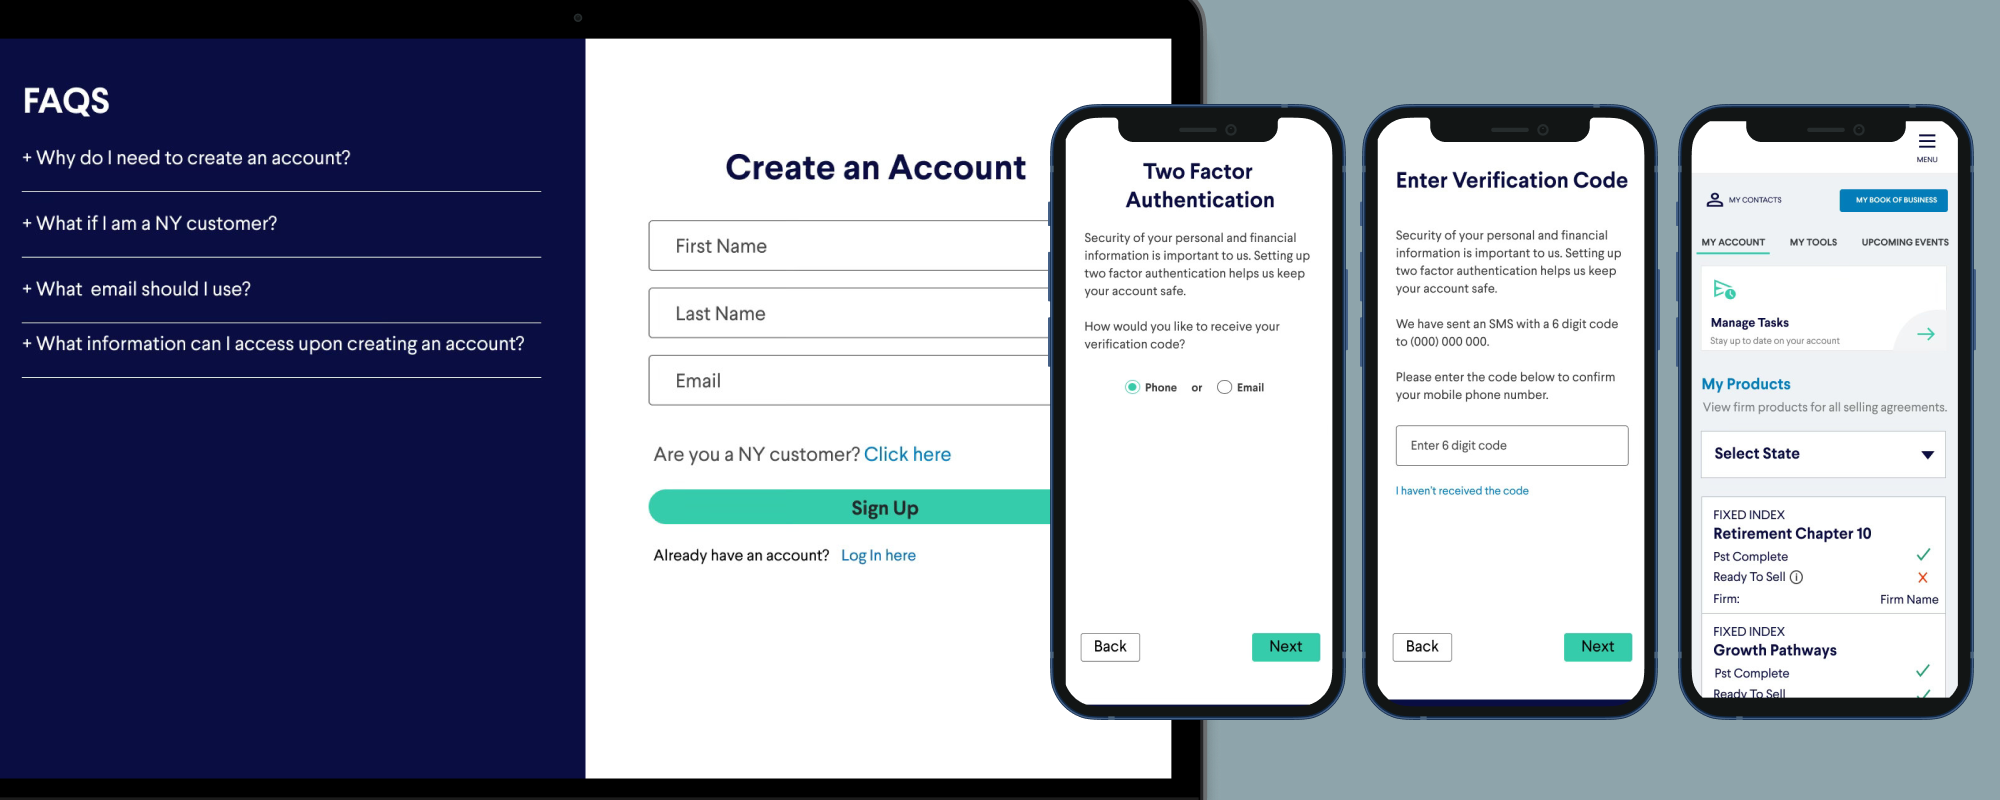
Single smart sign-in
One entry point for every user, with 2FA.
Role-adaptive dashboard
Content and permissions adjust to the user after sign-in instead of sorting them beforehand.
Contextual support
In-portal help surfaced based on the current task.
Unified business view
Policy portfolio visibility with state-level filtering for multi-state operators.
Outcomes
Results after launch.
Authentication success
Rose substantially after the unification.
Longer sessions
Users stopped bouncing between the wrong portals.
Less support
Call volume dropped meaningfully, helped by contextual help and fewer wrong-portal logins.
More feature use
Grew across roles as the dashboard showed users features they hadn't known they had.
Simple legacy access
Existing users kept simple policy access through the migration.